AI-powered GRC · risk and regulatory compliance management

Identifies obligations.
Prepares documents.
Monitors changes.

4Cyber GRC connects company information, internal documentation and processes with regulatory requirements. It identifies gaps, prepares documents and plans implementation steps. It then continuously monitors what needs updating.

AI processes the evidence and prepares proposed changes. An authorised person reviews and approves them.

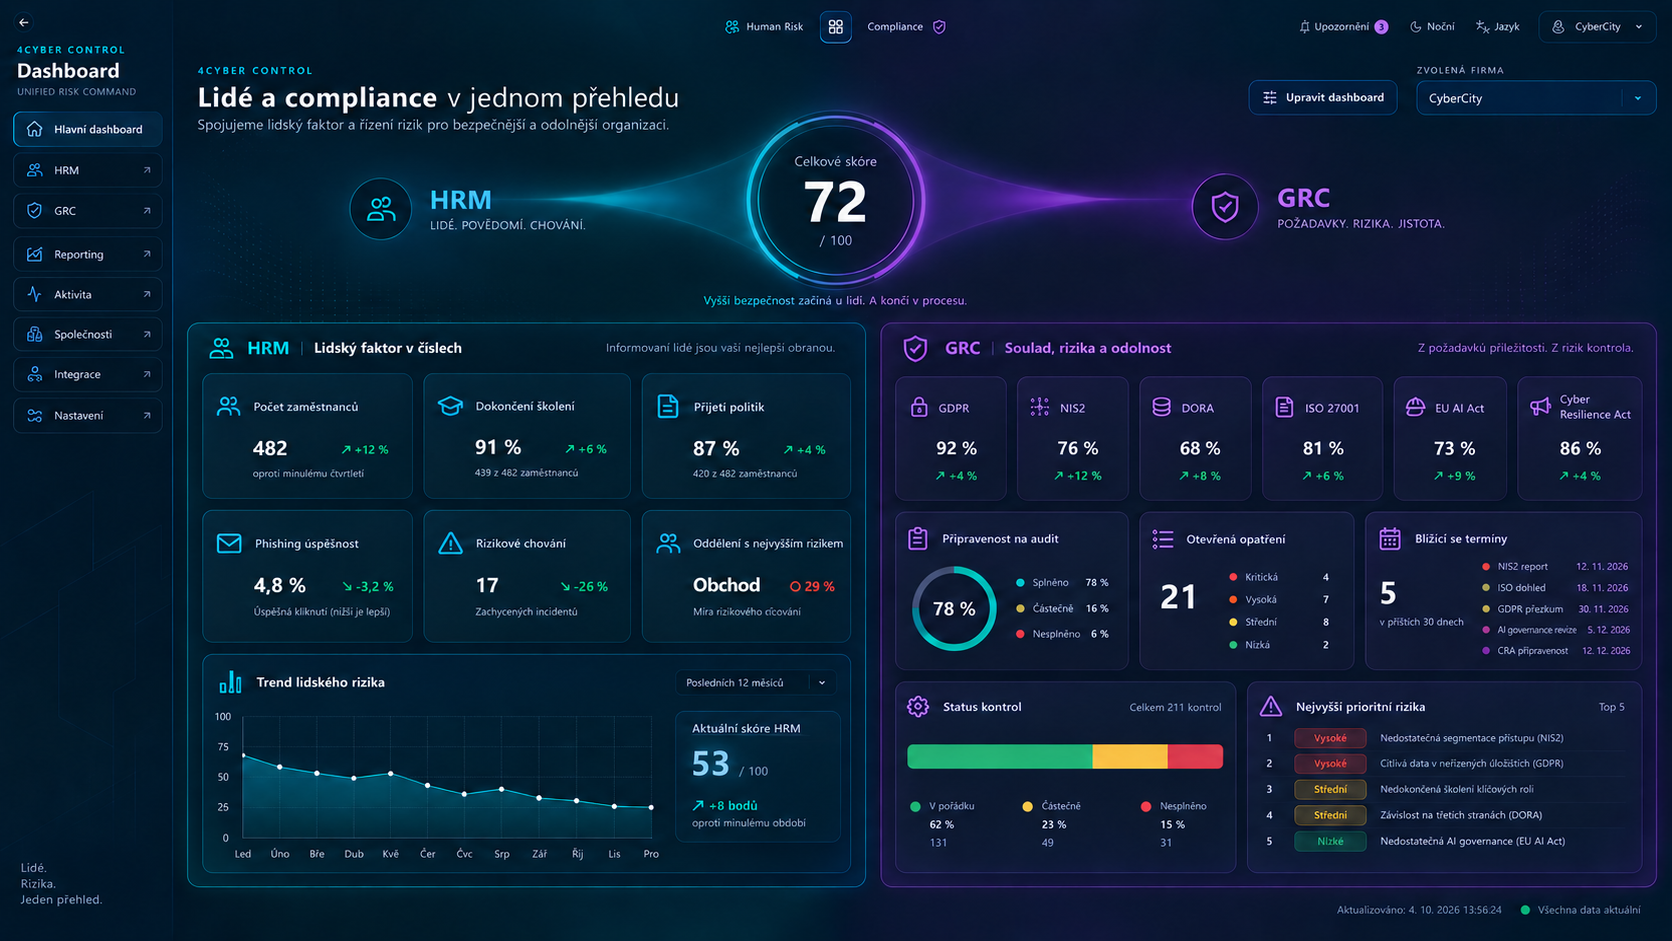
4Cyber unified dashboard: human risk, requirements and compliance status

4Cyber dashboard · a unified view of HRM and GRC
From initial assessment to continuous monitoring

Six steps.
One connected process.

First, the system gets to know your company. It then compares your current position with requirements, prepares the necessary documents and plans the next steps for your team.

01

Understands your company

Available public information forms an initial company profile. In the onboarding form, you add the necessary details about your activities, structure, systems and data handling.

Output: Your organisation’s profile and context.

02

Reviews documents and processes

Upload evidence or connect internal systems. AI analyses available documentation, policies and process information and links them to your company profile.

Output: A view of how your company actually operates.

03

Identifies relevant requirements

Based on your activities, size, systems and data, it assesses which supported regulations apply to your company and which requirements need to be addressed.

Output: Requirements linked to your specific company.Learn more

04

Assesses what is missing

Gap analysis compares your company’s current position with specific requirements. It distinguishes what is complete, missing or incorrect, and whether documentation matches internal processes.

Output: Gaps and their links to requirements.Learn more

05

Prepares solutions for approval

It creates missing documents and prepares amendments to existing ones. It also plans process changes and the implementation of measures, then submits the results to an authorised person for approval.

Output: Documents, amendments and an implementation plan.Learn more

06

Continuously monitors changes

It checks changes to monitored regulations every day and assesses their impact. It also responds to new information and changes within your company, preparing the related updates.

Output: Updates to documents and processes.Learn more

Regulations & Standards

Focus on what applies
to your company.

The system connects requirements with your documents and processes, so you can manage several compliance areas in one environment.

NIS2

Cybersecurity

GDPR

Personal data protection

AI Act

Artificial intelligence use

ISO/IEC 27001

Information security standard

DORA

Digital resilience

The scope is determined for each company. NIS2 is assessed in the Czech legislative context; ISO/IEC 27001 is an information security standard. Click a card to see its focus.

Gap analysis · requirements compared with reality

What is already in place.
What needs to change.

Gap analysis examines each requirement of a specific regulation. It connects requirements with documentation and process information to show where your company meets them and where remediation is needed.

  • What is complete and the evidence supporting it.
  • What is missing, incomplete or inconsistent with a requirement.
  • Whether documents reflect how the company actually operates.
  • Which documents and actions need to be added.
A clear result for every requirement

Meets requirementsBoth the document and the process meet the assessed requirement.
MissingThe required document, procedure or evidence is unavailable.
InconsistentDocumentation and the actual internal process contradict each other.
Needs updatingAn existing document needs amendment or expansion.
How gap analysis results are assessed.
AI prepares

Documents and specific amendments

It creates missing documentation, prepares corrections to existing documents and proposes the necessary process changes.

Your team approves

Review by an authorised person

Completed drafts are submitted to the responsible person for review, feedback and approval.

Your company implements

Actions, responsibilities and deadlines

An implementation plan is linked to identified gaps, allowing you to track progress in putting measures into practice.

Continuous compliance

Monitors regulatory changes.
And changes in your company.

Compliance does not end when documentation is approved. The system continuously assesses new information and prepares the necessary amendments as things change.

Daily monitoring

A regulatory change

Every day, it checks changes to monitored regulations. It assesses whether a change applies to your company and identifies the affected requirements, documents and processes.

RegulationsObligationsCompany impact
Continuous assessment

A change within your company

New internal policies, company structures, systems or processes may also change your obligations. Using new evidence and connected systems, it assesses what needs updating.

PoliciesCompany structureSystems and processes
A specific change → specific amendments for approval

The system prepares related documentation amendments, proposes process changes and plans their implementation. Approval remains with an authorised person.

Document updatesProcess amendmentsImplementation steps
Coming soon · in development

AI and AI agent governance

AI in your company.
With clear rules.

We are also extending the platform to cover AI and AI agent governance. The aim is to connect an inventory of tools, their owners, permissions and rules with corporate processes and compliance requirements.

This area is currently in development. During a demo, we can discuss the planned direction and your organisation’s needs.

Planned development

An inventory of AI tools and agentsWhere they are used, what they do and who is responsible for them.

Rules and permissionsWhich data they can work with and which actions they are allowed to take.

Oversight and recordsRisk assessment, activity monitoring and evidence for reviews.

Coming soon. These features are not yet part of the current offering.

Frequently asked questions

GRC without
unnecessary complexity.

What do GRC and compliance mean?

GRC brings together governance, risk management and compliance. Compliance means meeting the regulations and other requirements that apply to your organisation.

How does implementation in our company begin?

The system creates an initial profile from available public information. You complete and verify it in the onboarding form, then provide internal evidence or connect corporate systems for further analysis.

Do we have to create documentation from scratch?

No. The platform uses your existing evidence. Based on the gap analysis, it creates missing documents and prepares amendments to those that are incomplete, incorrect or inconsistent with internal processes.

Who approves documents and changes?

AI submits completed drafts to an authorised person in your company. They review them, provide feedback where needed and approve them. Implementation steps follow the approved changes.

What happens when a regulation or our company changes?

The system assesses the impact on your organisation and related requirements. It prepares the necessary document updates, proposed process changes and implementation steps for approval.

Where is our internal data processed?

Customer data remains on internal servers in the Czech Republic at the Algotech data centre. A closed AI agent processes it; it is not sent to public AI services. The US parent company has no access to it.

4Cyber platform demo

See GRC
in the context of your company.

We will walk you through the journey from your company profile and gap analysis to prepared documents, approvals and continuous updates.

Book a GRC demo ↗